Aegis
AI-assisted security assessment.
On your terms — and only in scope.
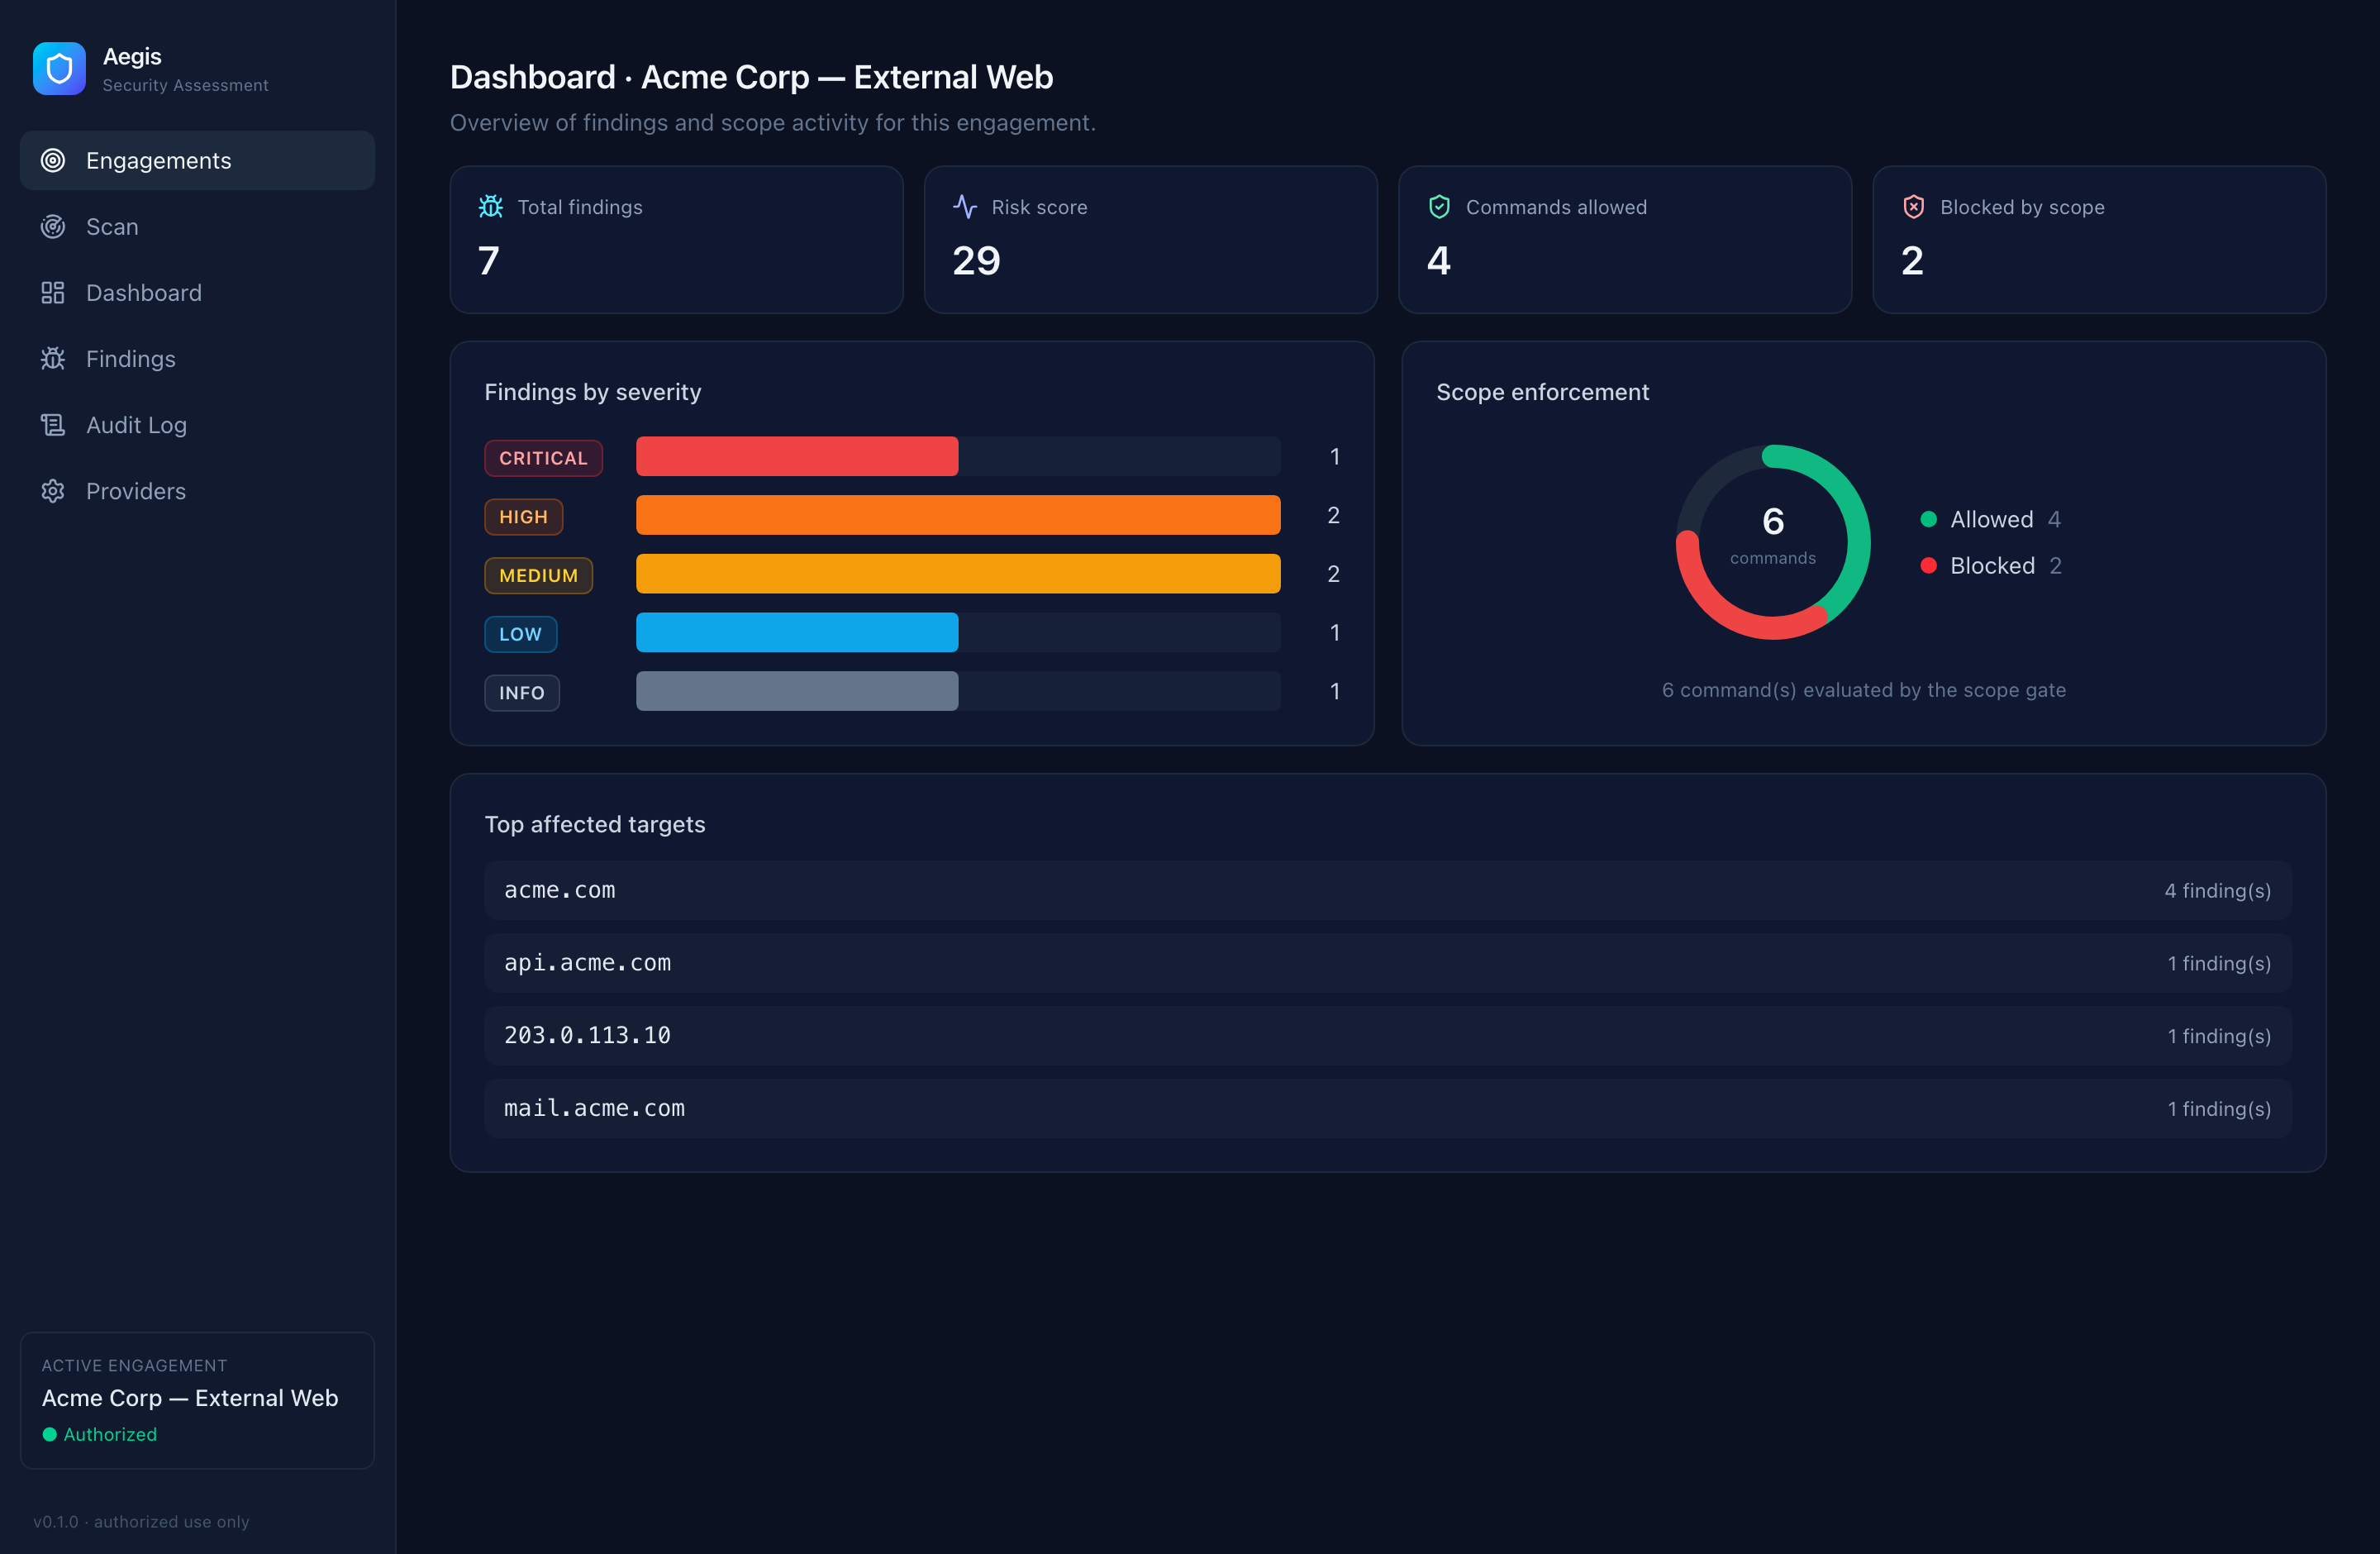
Enforced scope engine
Authorized. By design.
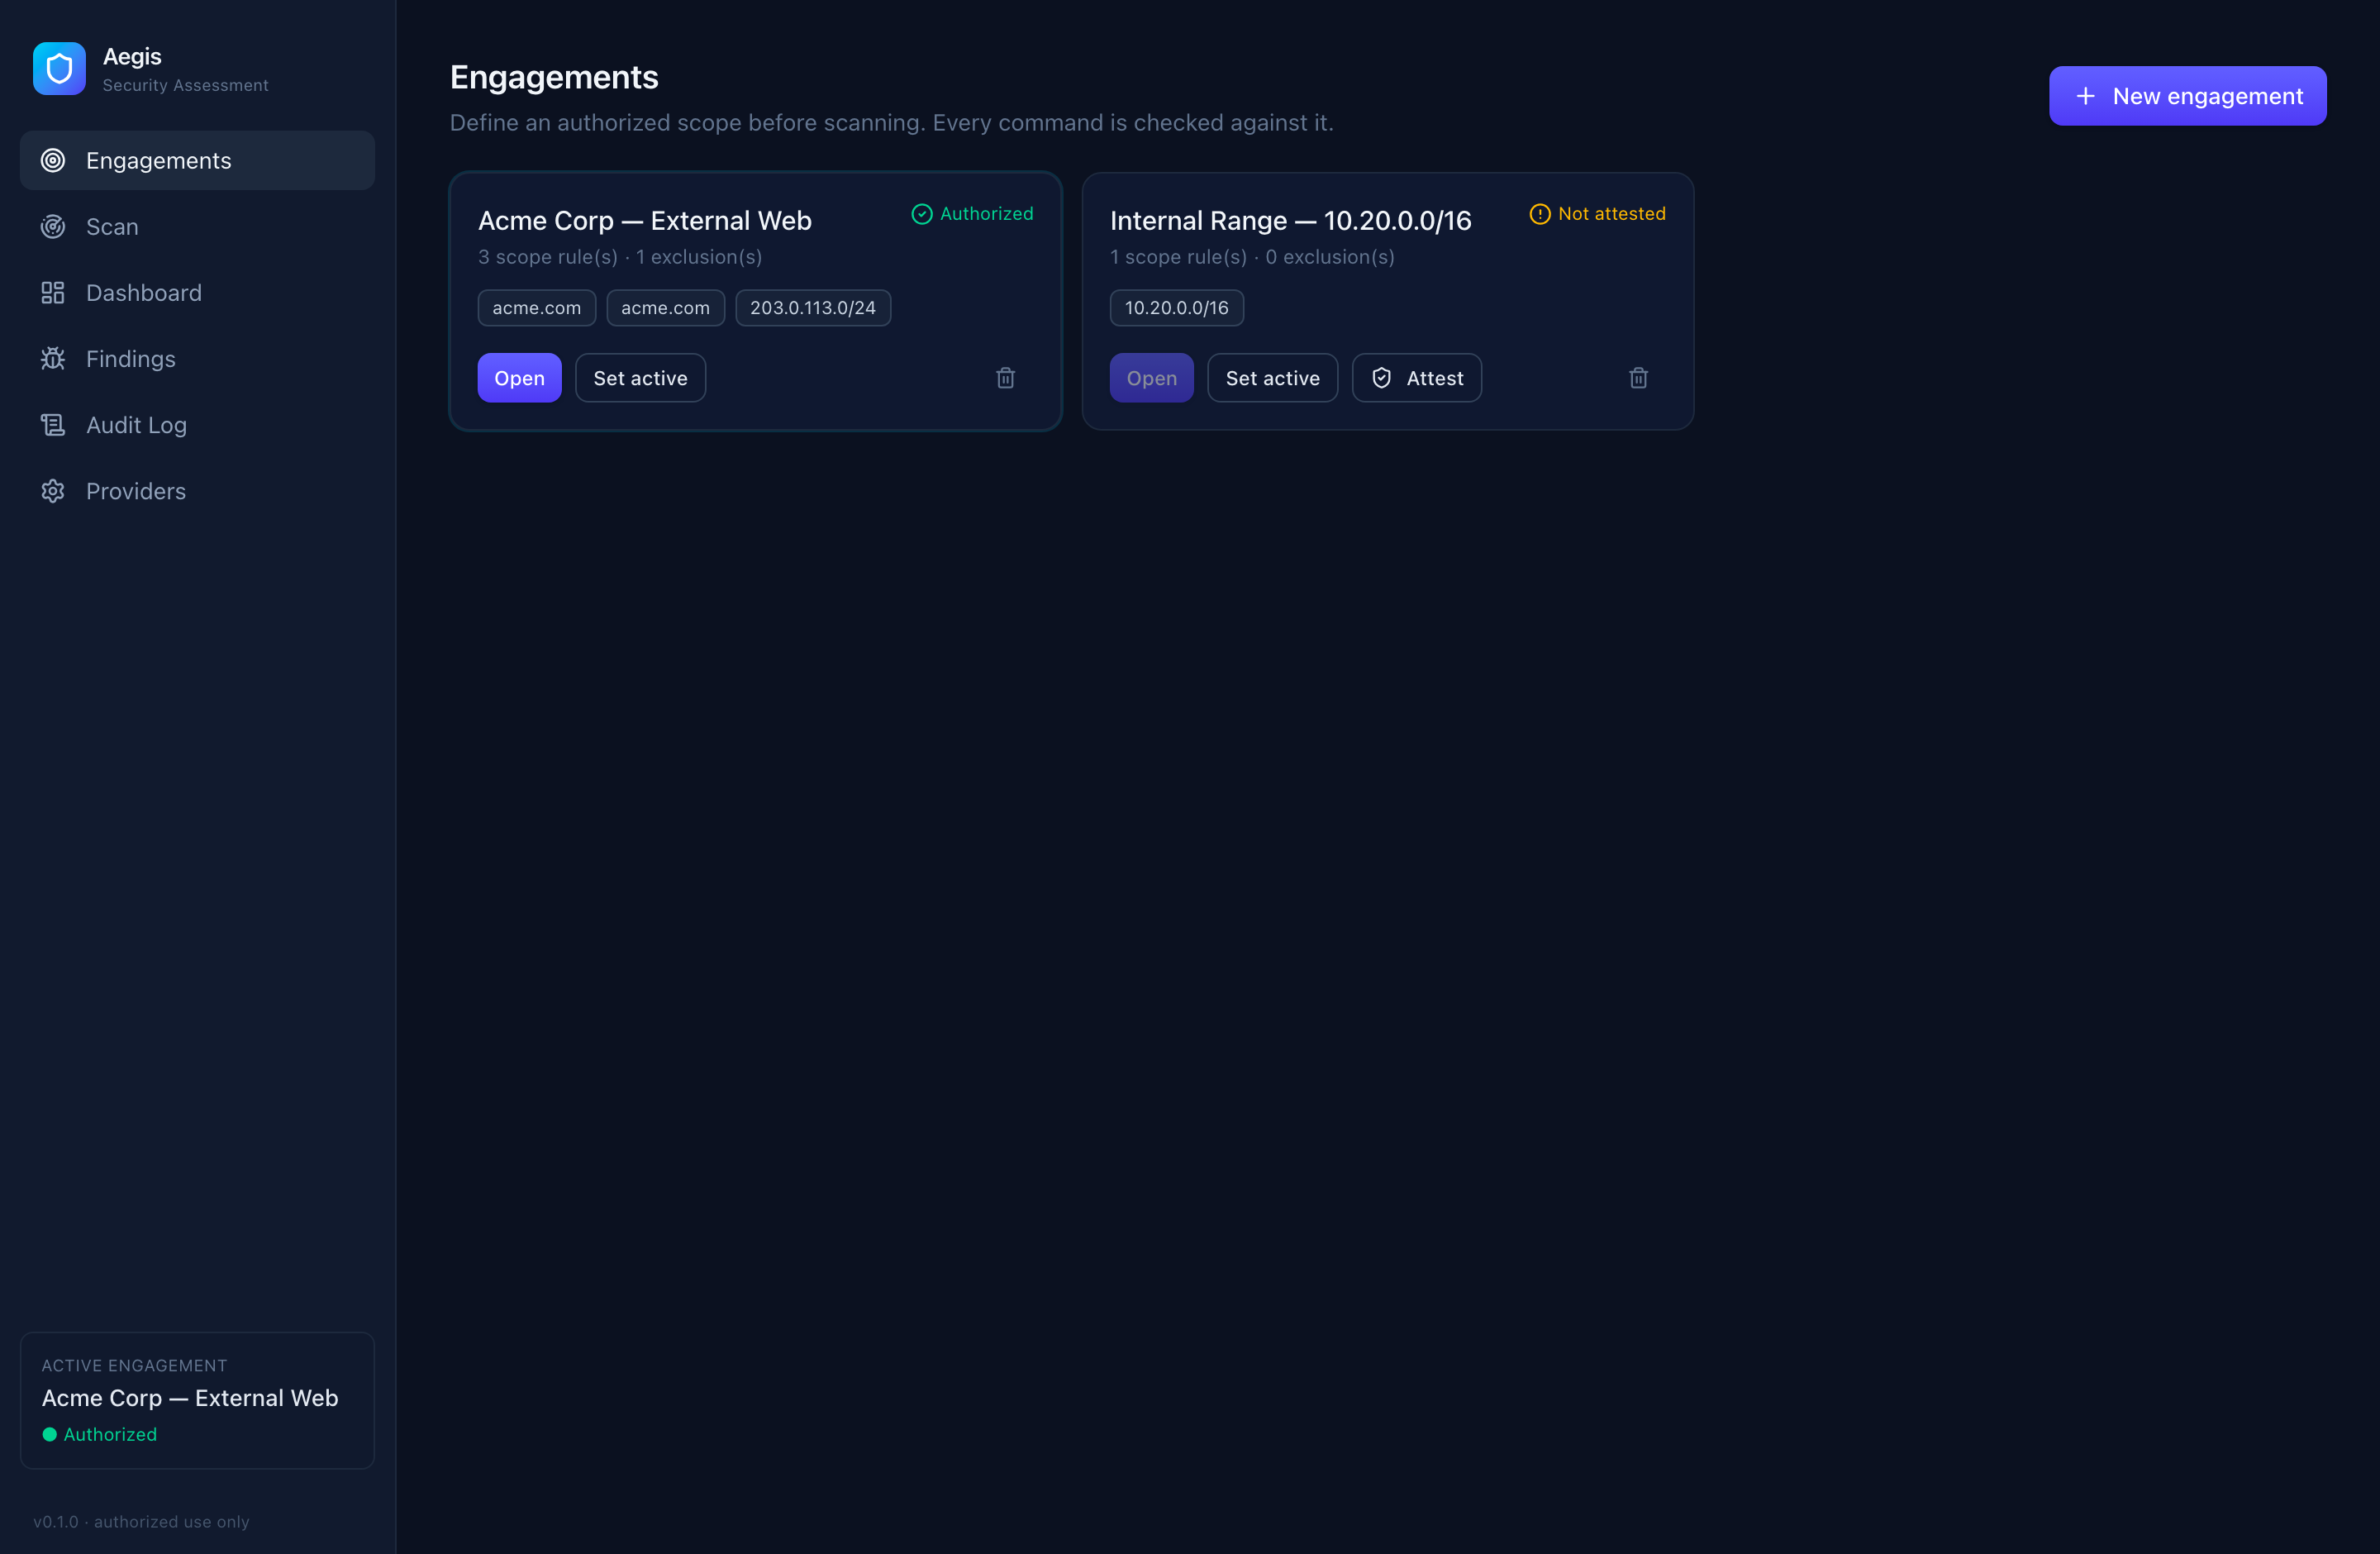
Declare the targets you're permitted to test. Every command — whether you type it or the AI proposes it — is parsed for its targets and blocked before it runs if anything is out of scope. A hard, code-level guardrail, not a prompt. Every decision is logged.
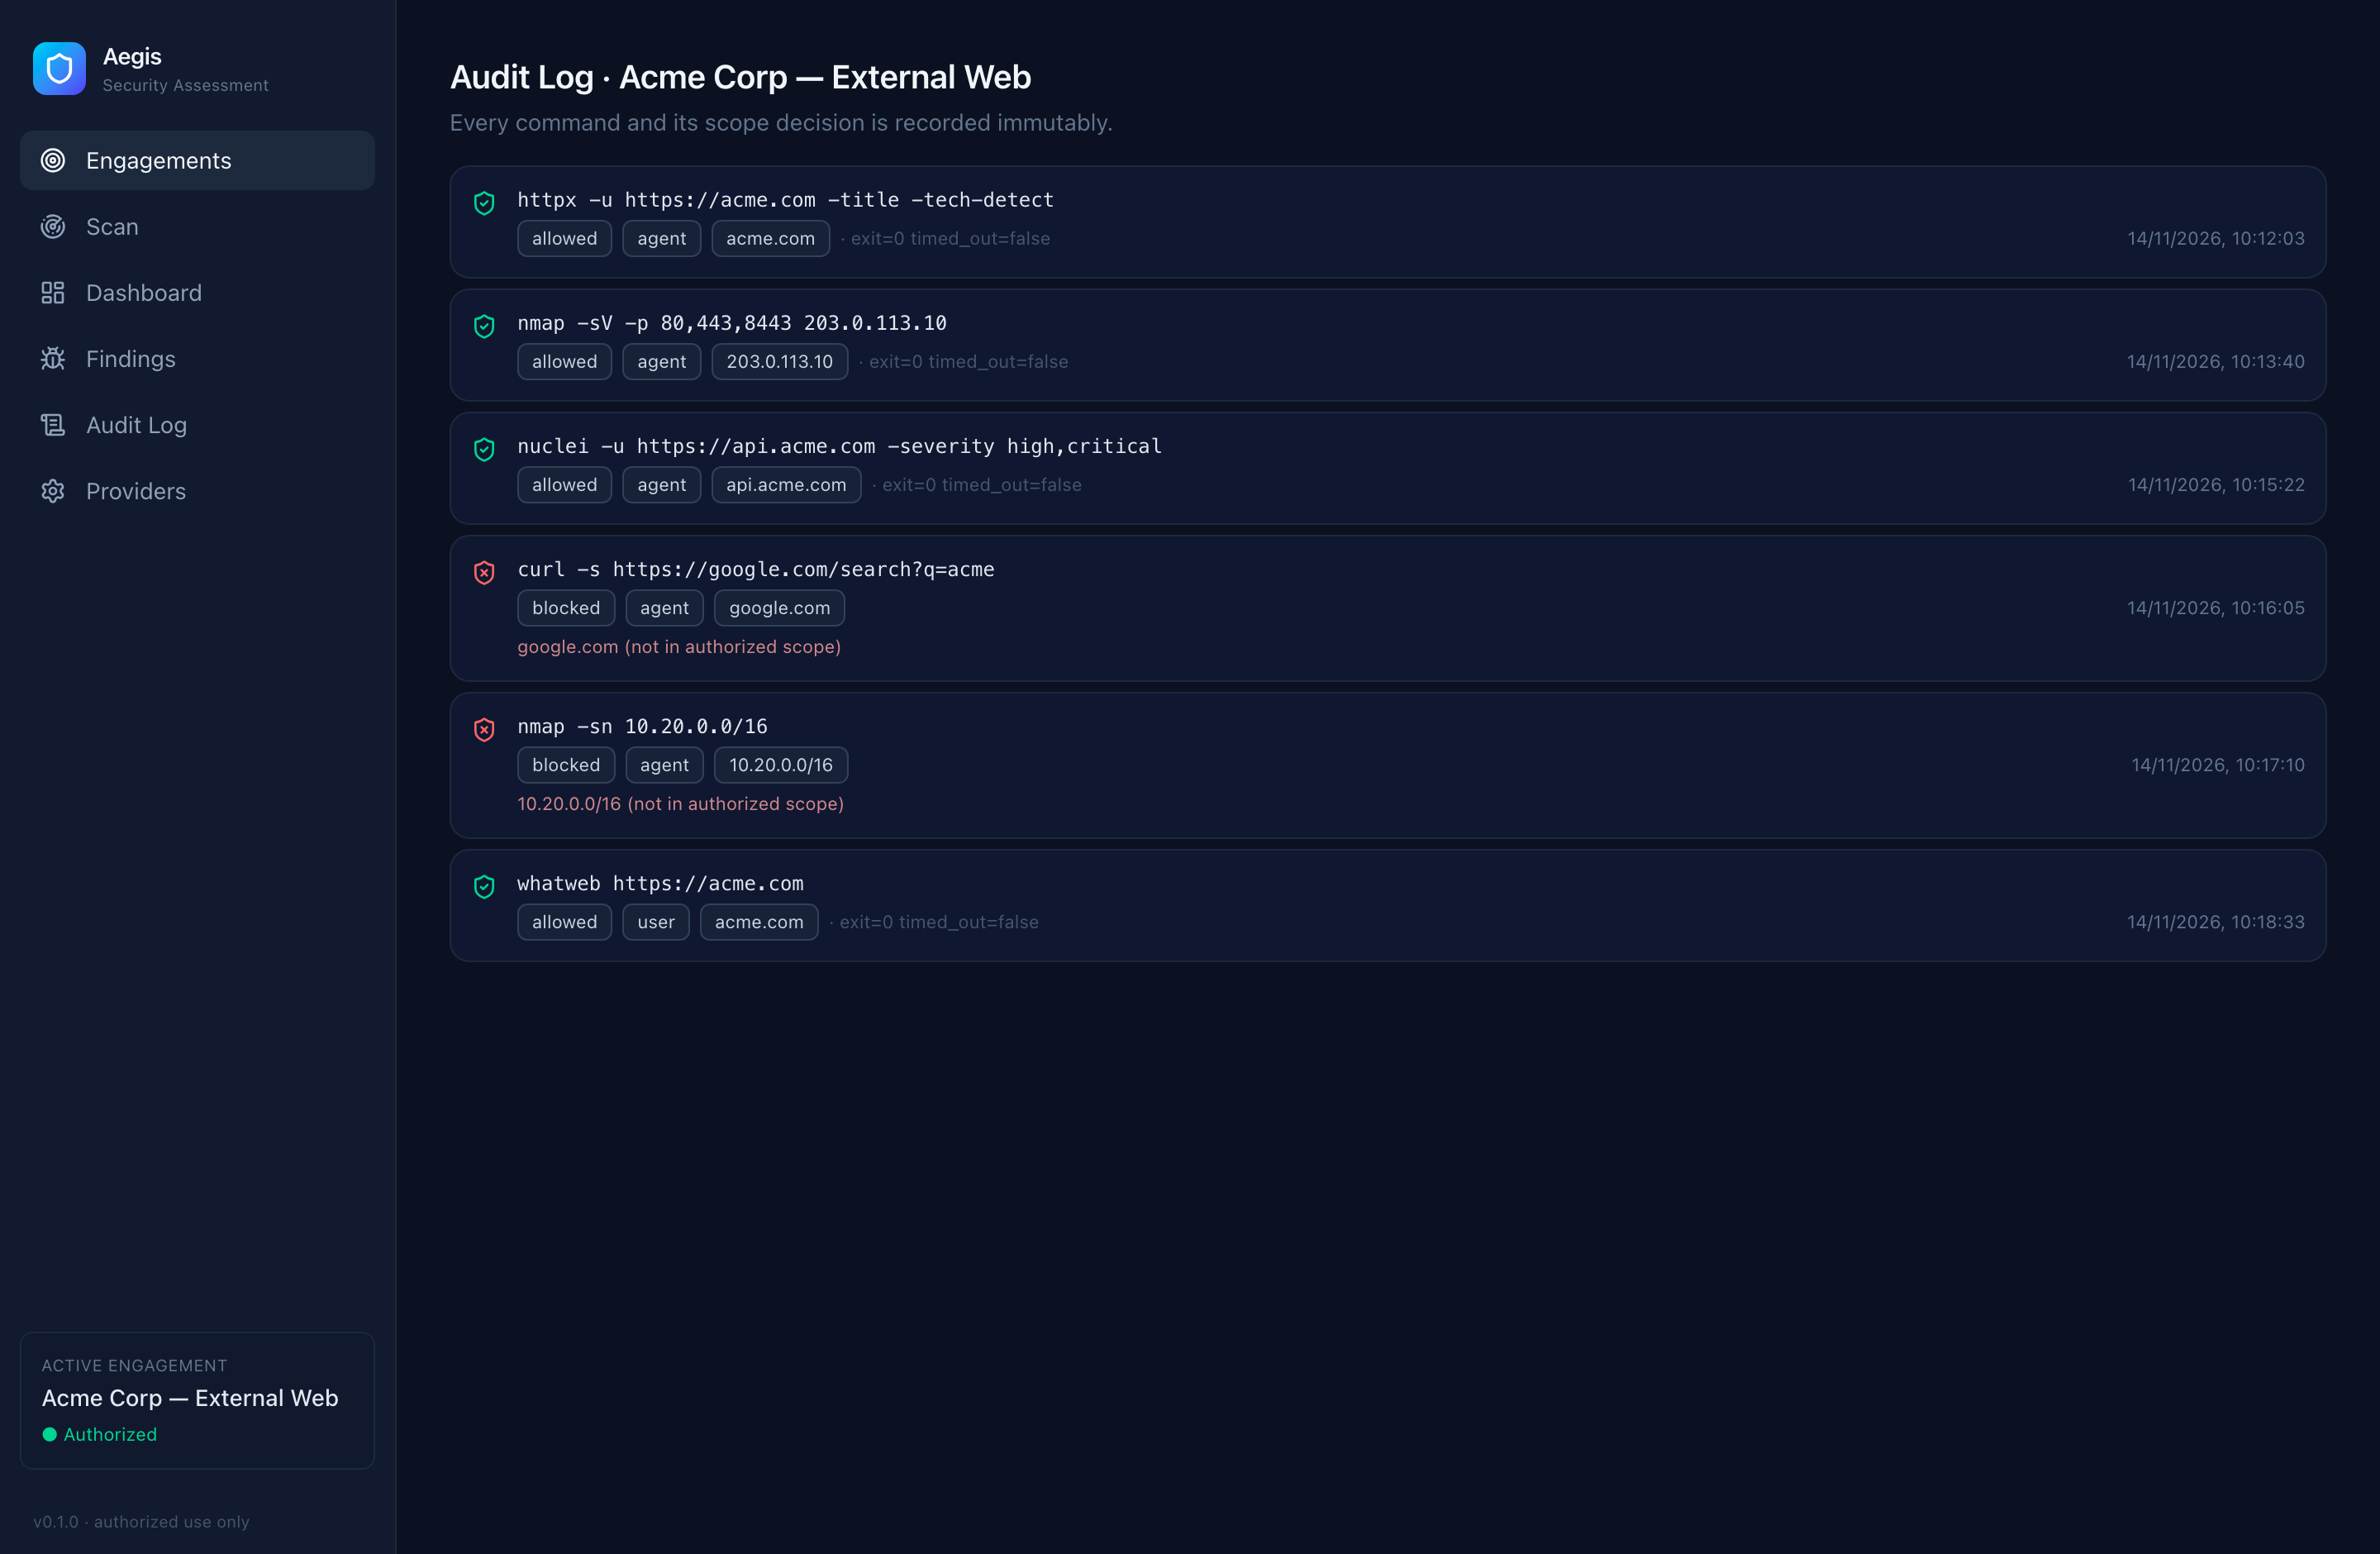
Multi-provider AI
Every major model.
One cockpit.
OpenAI, Anthropic, Azure OpenAI, OpenRouter, LiteLLM, Ollama and any OpenAI-compatible endpoint. Keys stay in your OS keychain — never on disk, never in the cloud.
Isolated sandbox
Runs in a box. Never on your host.
Industry-standard scanners run inside a disposable Docker container with hard timeouts, streaming live to the app. Autonomous by default — with a step budget and a kill switch — plus an Assisted mode that asks before every command.
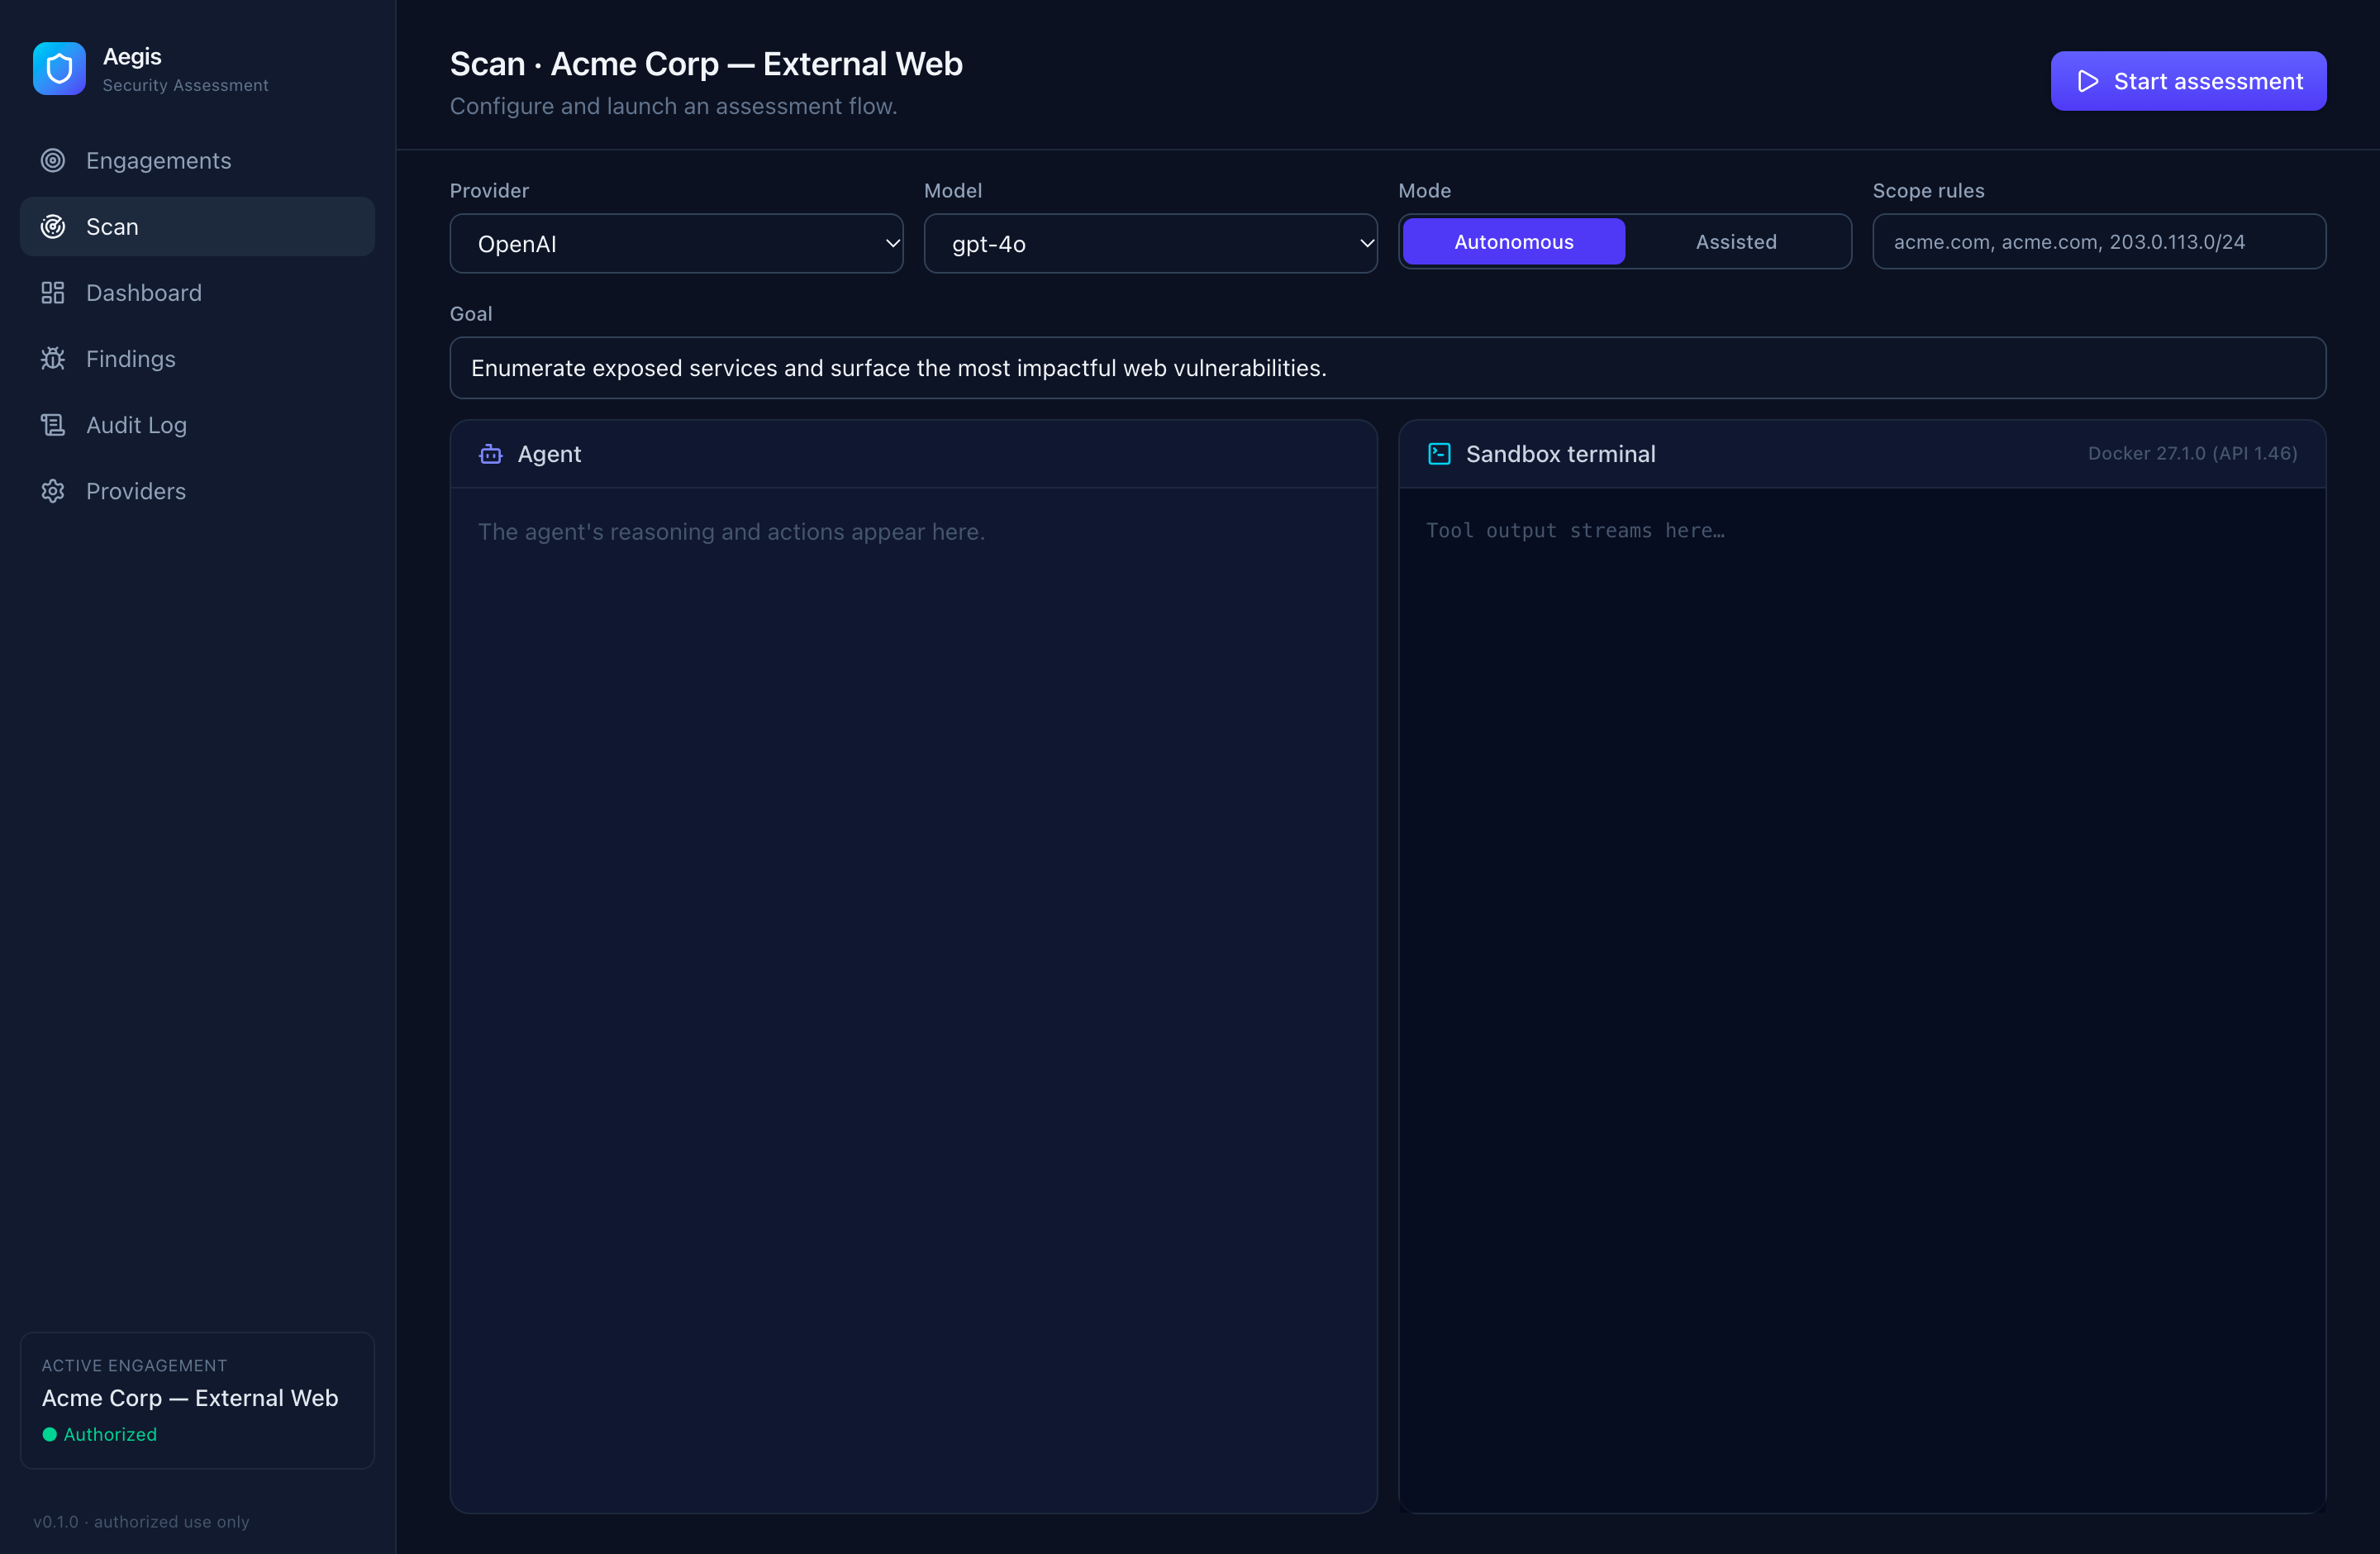
From signal to story
Scan. Triage. Report.
The AI normalizes raw tool output into severity-ranked findings with evidence, CWE/CVE and remediation — then exports a clean Markdown or PDF report, command audit trail included.
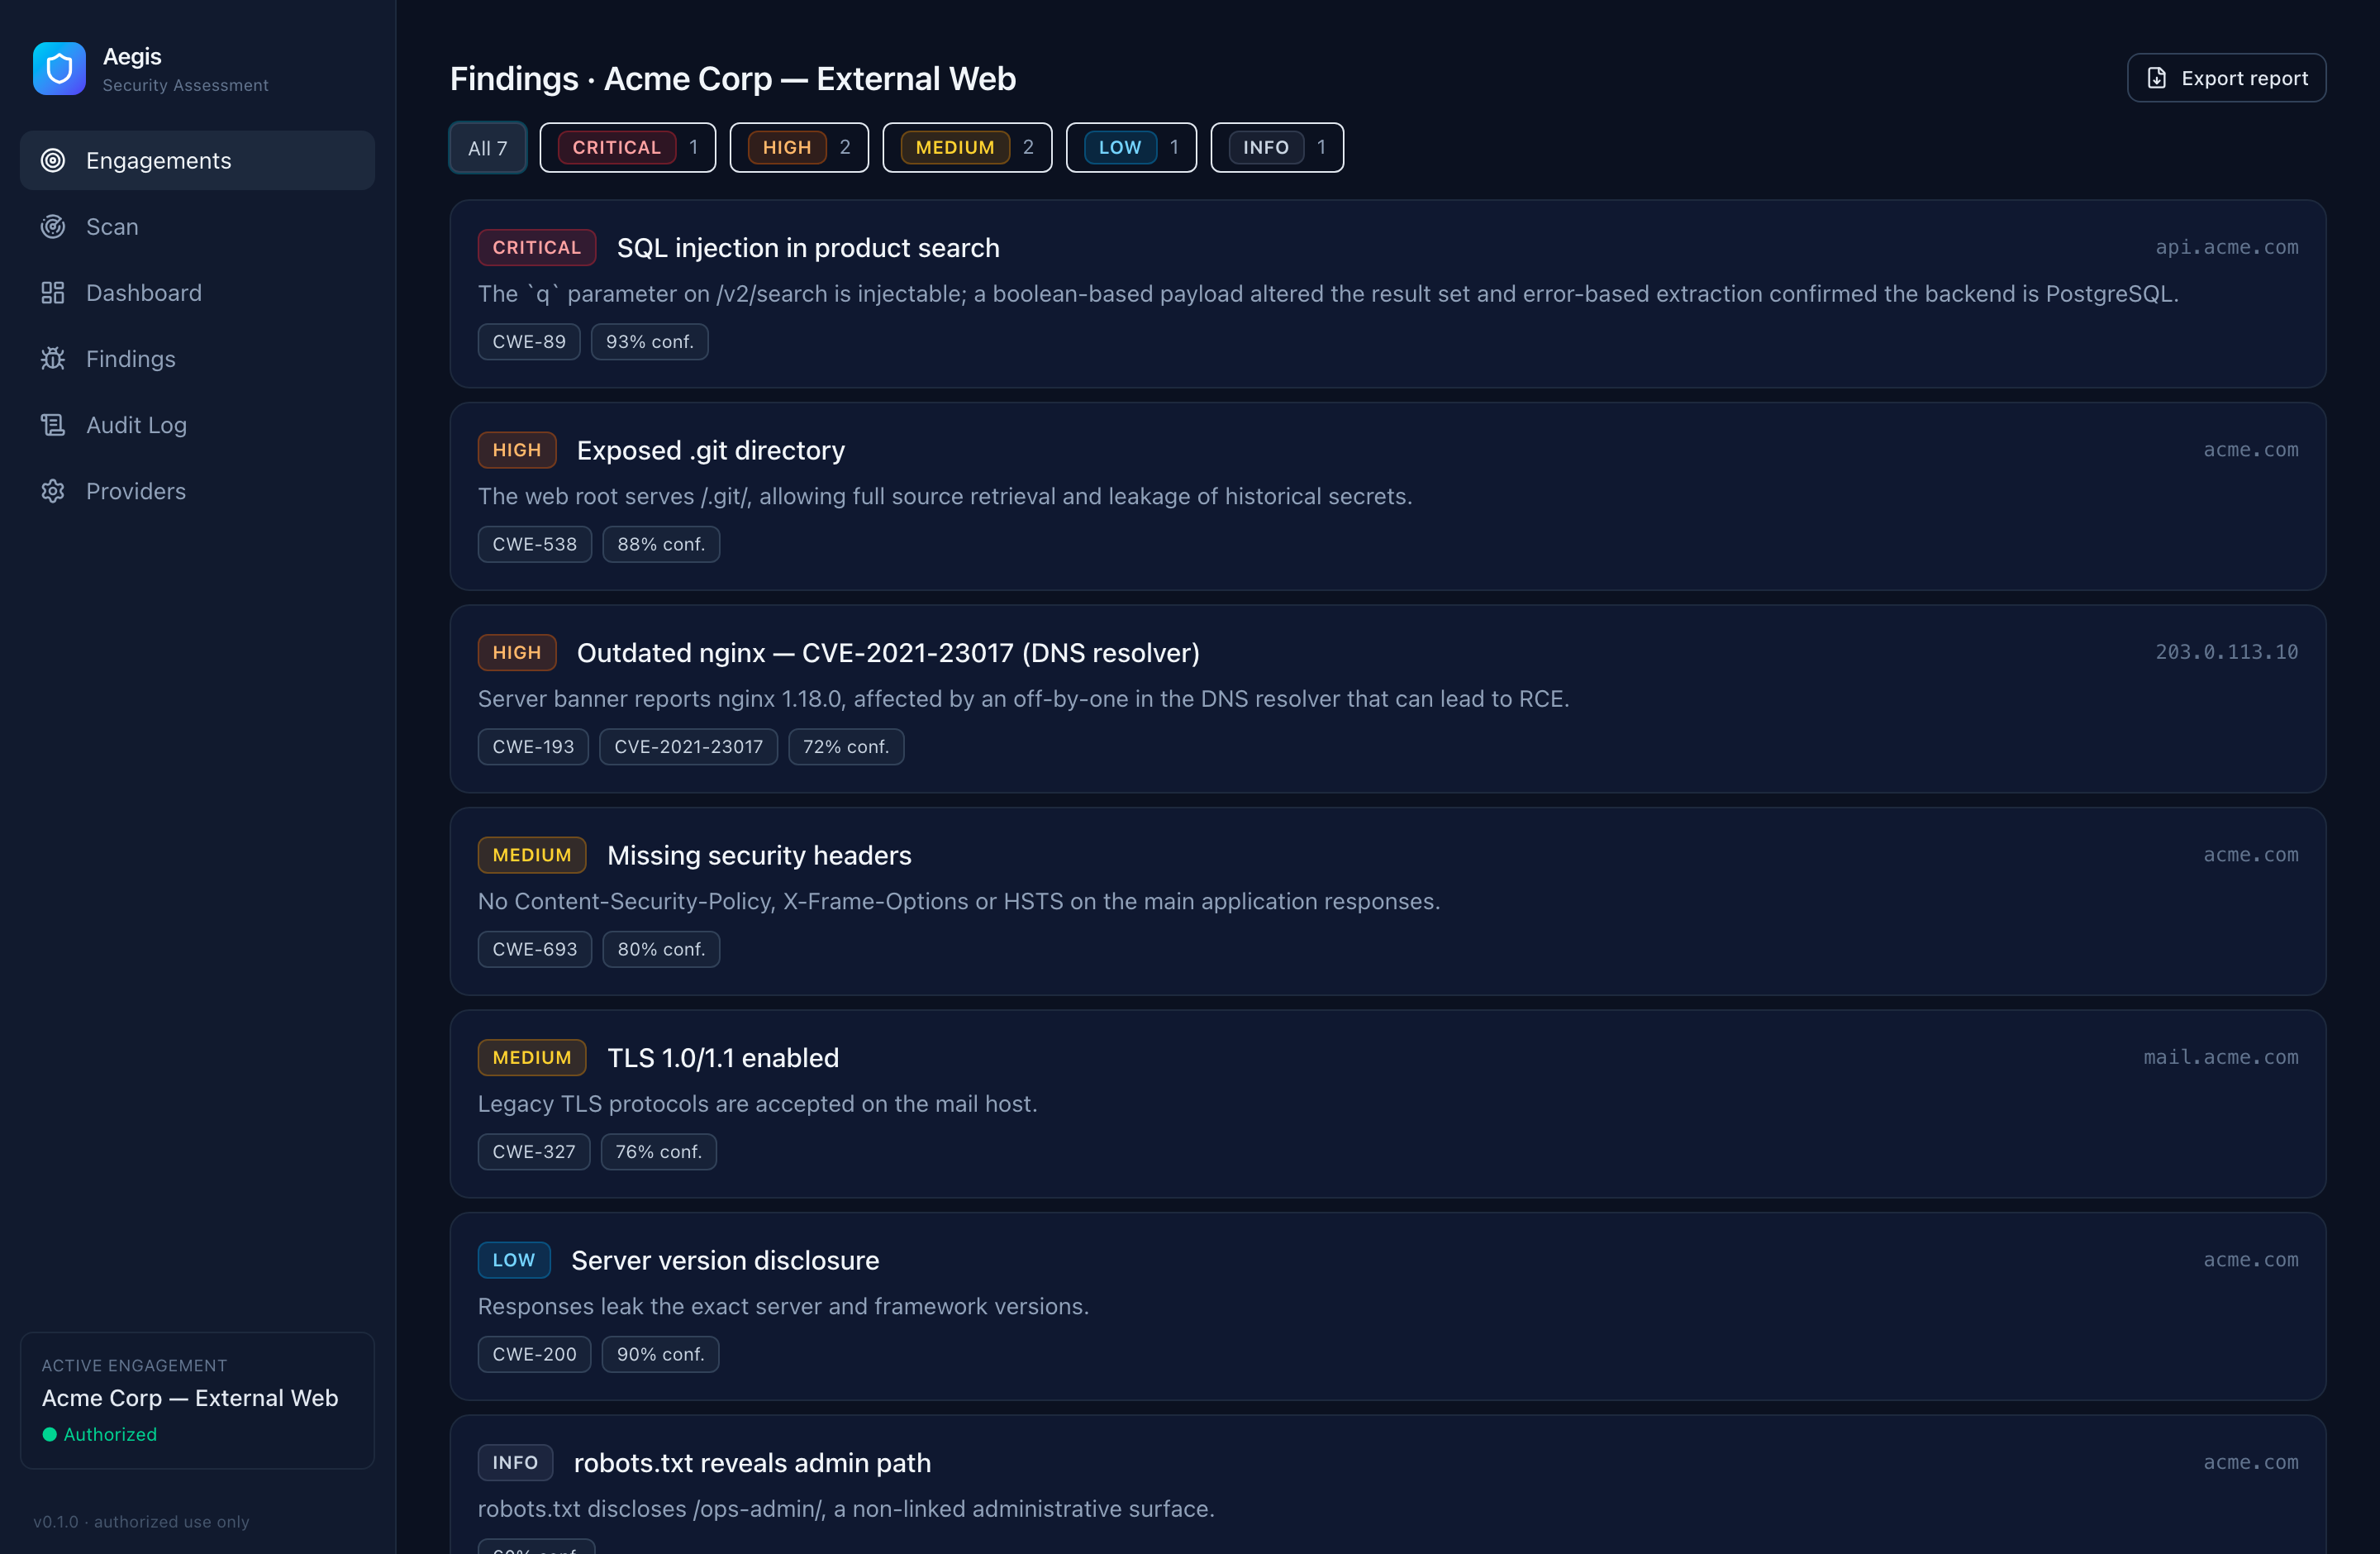
How you use it
Four steps from authorization to report.
Define the engagement
List your authorized targets and attest you're permitted to test them.
Connect an AI provider
Add OpenAI, Anthropic, Ollama or any OpenAI-compatible endpoint. Keys stay in your keychain.
Run the assessment
Autonomous or Assisted. Tools run sandboxed and scope-gated, streaming live.
Review & export
Triaged findings, a risk dashboard, and a one-click Markdown or PDF report.
A closer look
Get Aegis.
Free and open source. Built with Tauri — a small, native desktop app.
Apple Silicon · requires Docker Desktop for scanning